On 25 February 2025, Singapore’s Infocomm Media Development Authority (IMDA) published two Advisory Guidelines on the Resilience and Security of Data Centres (DC Guidelines) and Cloud Services (CS Guidelines) (collectively, the Advisory Guidelines). The Advisory Guidelines provide guidance and a set of best practices for data centre operators (DCOs) and cloud service providers (CSPs) to minimise service disruptions and mitigate risks pertaining to their operations. As these Advisory Guidelines are potentially a precursor to the forthcoming Digital Infrastructure Act (DIA), DCOs and CSPs are advised to implement the Advisory Guidelines’ best practices to stay ahead of future compliance requirements.
Summary of the DC Guidelines
The DC Guidelines identify key categories of risk relating to infrastructure, governance and cyber that may compromise the security and resiliency of data centres. Examples include:
| Examples of Security and Resiliency Risks Facing Data Centres | |
| Infrastructure risks |
|
| Governance risks |
|
| Cyber risks |
|
To address these risks, and to bolster DCOs’ resilience and service continuity in the event of unforeseen disruptions, the DC Guidelines recommend that DCOs implement a business continuity management system (BCMS) which enacts a continuous process loop of “Plan”, “Do”, “Check”, and “Act”.
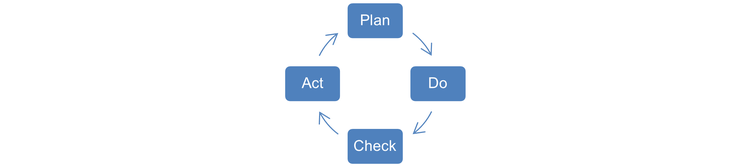
The DC Guidelines provide guidance on specific action items DCOs can undertake with respect to each stage of a BCMS:
| Key Action Items for DCOs under Business Continuity Management System (BCMS) | ||
| (1) PLAN | Objective | Establish scope and policies of BCMS. |
| Action Items |
|
|
| (2) DO | Objective | Implement and operate BCP, including its controls, processes and procedures. |
| Action Items |
|
|
| (3) CHECK | Objective | Monitor and review BCMS performance against its goals and objectives. |
| Action Items |
|
|
| (4) ACT | Objective | Improve and update BCMS. |
| Action Items |
|
|
Summary of the CS Guidelines
Similarly, the CS Guidelines identify key security and resiliency risks facing CSPs and recommend that CSPs implement a set of measures (based on industry standards such as Multi-Tier Cloud Security, ISO 27001 and the Cloud Security Alliance’s Cloud Controls Matrix) to mitigate these risks:
| Category | Recommended Measures |
| Cloud Governance |
|
| Cloud Infrastructure Security |
|
| Cloud Operations Management |
|
| Cloud Service Administration |
|
| Cloud Service Customer Access |
|
| Tenancy and Customer Isolation |
|
| Cloud Resilience |
|
Key Takeaways and Recommendations
- DCOs and CSPs are encouraged to implement the measures recommended by the Advisory Guidelines. While voluntary, the Advisory Guidelines provide a set of best practices for DCOs and CSPs and establish a baseline that will likely form the foundation for mandatory requirements under the upcoming DIA.
- The publication of these Advisory Guidelines is timely. Recently, in 2024, Singapore announced plans to expand its data centre capacity following the relaxation of a moratorium on new data centre developments previously imposed in 2019. This expansion is part of a broader strategy to support the growth of the digital economy while ensuring sustainable practices.
- At the same time, these policy shifts which aim to expand data centre capacity and attract further capital have been accompanied by increased regulation. Regulatory scrutiny of the data centre and cloud services industries is increasing and DCOs and CSPs should keep track of legislative and policy developments.
- In addition to the Advisory Guidelines, the amendments to Singapore's Cyber Security Act 2018 expand regulatory oversight to cover the cybersecurity of DCOs and CSPs, particularly those providing foundational digital infrastructure, requiring them to adhere to cybersecurity standards and report incidents to the Cyber Security Agency of Singapore. DCOs and CSPs must ensure compliance not only for their own systems but also for third-party infrastructure used by essential service providers. Non-compliance can result in significant civil penalties of up to 10% of the entity's annual turnover in Singapore, emphasising the importance of robust cybersecurity practices for DCOs and CSPs.
- The anticipated growth in the data centre and cloud services sectors, driven by the increasing demand for AI-centric applications, present a significant opportunity for businesses. By adopting the Advisory Guidelines, DCOs and CSPs can position themselves as secure and resilient during a time when cyber attacks from threat actors are on the rise, and attract clients who value data protection and cybersecurity. Prominent stakeholders in the DC and CS sectors have already publicly endorsed the Advisory Guidelines, showcasing their commitment to industry-leading practices in security and resilience.
- DCO and CSP customers are advised to update their due diligence processes when selecting or renewing contracts with DCOs and CSPs to ensure alignment with these new guidelines and potential future regulatory requirements. Customers may consider imposing additional contractual obligations on contracting DCOs and CSPs who have not implemented the Advisory Guidelines.
We would like to thank Jainthan Jayaretnam for his assistance in preparing this article.